Security Response
Threats Detected. Actions Taken. In Seconds.
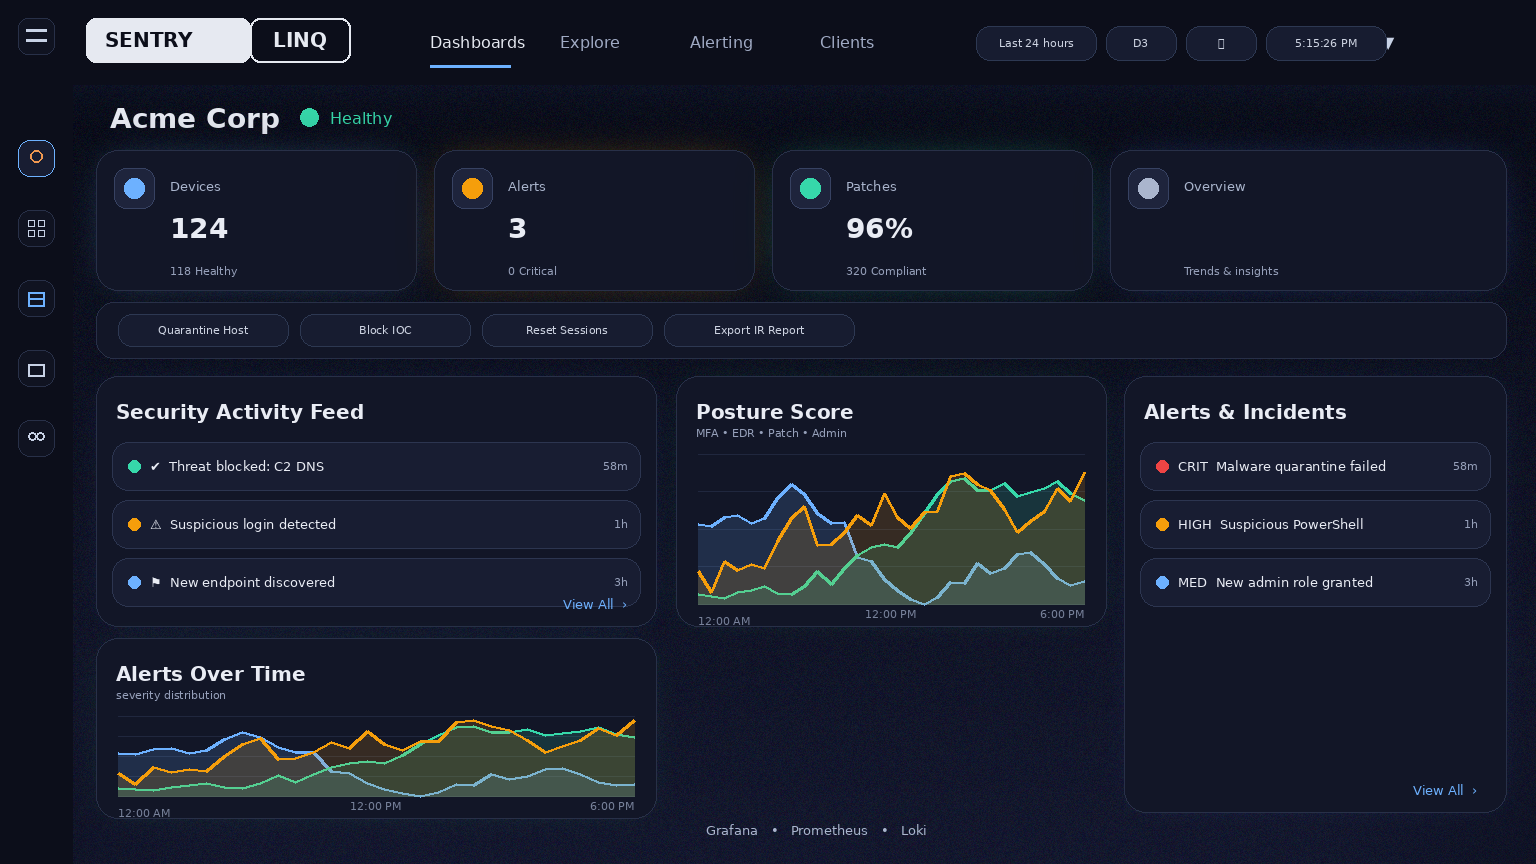
SIEM integration, auto-quarantine, malware removal, IOC blocking, incident timeline, and alert escalation.
Auto-Response Actions
✓Quarantine infected host
✓Block malicious IP/domain
✓Revoke compromised credentials
✓Isolate affected network segment
✓Generate IR report
✓Alert security team via Slack/Teams
Human-in-the-Loop
Critical actions always require approval. SentryLinq recommends the action, but you decide whether to execute. No automated changes to critical systems without your sign-off.
Ready to Put IT on Autopilot?
Start your free 14-day trial. No credit card required.